Knocknock — Session Authentication for Go
A lightweight Go library for managing authentication sessions: cookie/header/query-param as the token source, a pluggable store, and ready-made HTTP middleware.
A lightweight Go library for managing authentication sessions — without forcing you to use a specific store or web framework.
The Problem
In most small Go services, authentication gets solved either by a heavy framework or by copy-pasting the same code from project to project: generating a token, reading it from a cookie/header, middleware for protected routes. Knocknock moves that routine into a separate module with a minimal API.
Architecture
The interaction with the library is illustrated in the diagram:
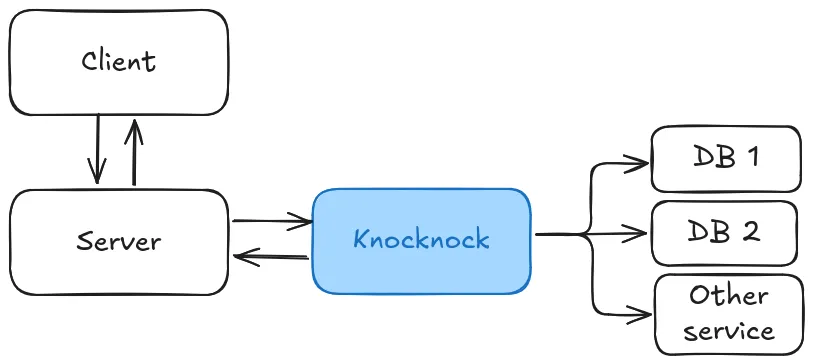
The library is built around the Store interface — it’s responsible for storing sessions and isn’t tied to any particular database:
type Store interface {
	Save(ctx context.Context, session *Session) error
	Get(ctx context.Context, token string) (*Session, error)
	Delete(ctx context.Context, token string) error
}
Knocknock provides a MemoryStore for development; for production, plug in any implementation of your own. The token source (cookie, HTTP header, or query parameter) is configured via functional options — the middleware checks all the sources itself, in order, so the frontend doesn’t need to know exactly where the server expects the token.
How to Run
Install the library the native Go way:
go get -u github.com/tolstovrob/knocknockThen, in your project:
store := knocknock.HandleMemoryStore()
auth := knocknock.HandleAuth(store, knocknock.WithDefaultExpiry(24 * time.Hour))

handler := auth.Middleware()(mux)
You can browse the full API via go doc -http — the package is fully documented.